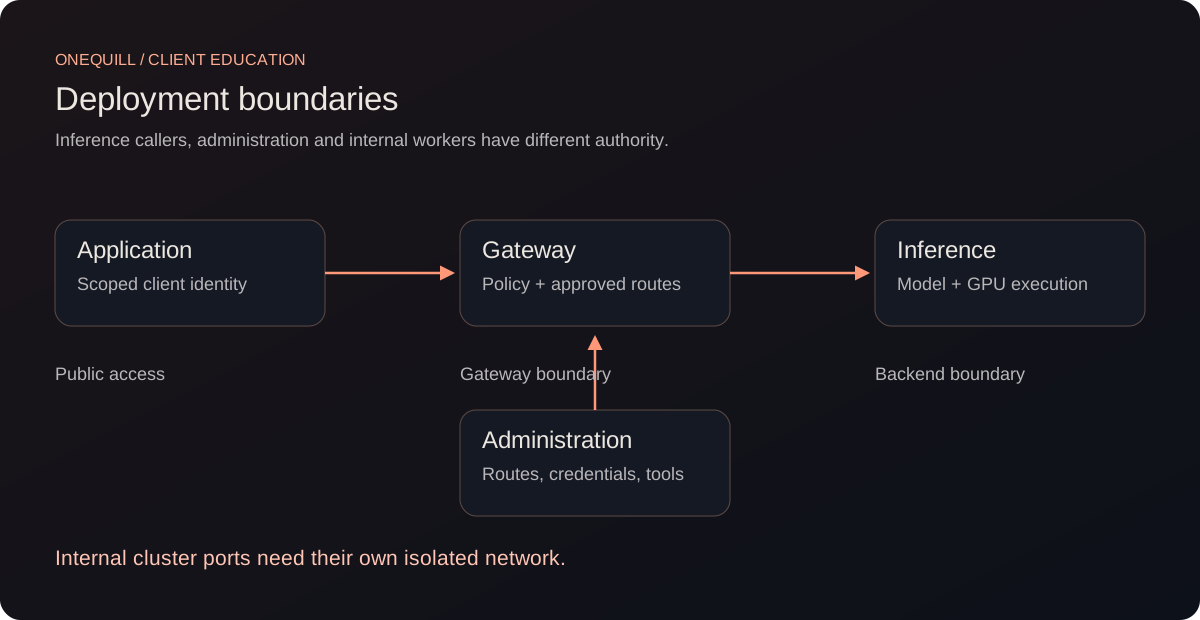
A route that is syntactically valid can still cross an ownership boundary. Credential-backed resources require authorisation for every route and policy reference, not just for the namespace that supplies the frontend.
What deployment does this concern?
Component and scope: Cross-namespace backend references authored by Kubernetes namespace administrators.
Affected versions / scope: < 1.3.0; configuration also matters after upgrade.
Vendor remediation: 1.3.0 plus AGW_BACKEND_REF_GRANT_MODE=route-and-policy
A tenant namespace administrator can author Gateway, HTTPRoute or Policy resources that refer to credential-bearing backends in another namespace. The vendor describes a multi-tenant control-plane issue and no remotely exploitable surface.
Vendor response and practical action
The vendor requires the patched release together with route-and-policy backend-reference grant enforcement. The default route mode alone is insufficient for the described policy-reference condition.
Treat the vendor notice as the starting point for an applicability decision. Identify the installed artifact and configuration, document whether the prerequisite exists, and assign an owner to any required change. A public advisory does not establish that your installation was exposed or that a managed service shares the same condition.
What clients can learn
Patch status is a release-and-configuration claim. Record the environment setting, accepted resources and cross-namespace authorisation evidence beside the version number.
A useful evaluation result connects a named control to evidence from the actual deployment. Keep the provider's statement, your effective configuration and a relevant demonstration together. If the result depends on a feature being disabled or a network being isolated, retain that fact with the version number so a later change triggers review.
Questions to take to your provider
- Who may create routes and policies in each namespace?
- Are route and policy backend references both subject to grants?
- Is AGW_BACKEND_REF_GRANT_MODE set to route-and-policy?
- Can a tenant use a backend credential owned by another namespace?
Use the six-page evaluation worksheet to record evidence, ownership and actions. Continue with AI gateway security: protect the boundaries that matter for the wider evaluation context.
Technical detail: evidence and identifier limits
An internet caller without control-plane permissions is outside the described prerequisite. Do not present this case as an unauthenticated network attack.
Evidence label: security advisory. Source-review date: 2026-10-07. Source publication or event date: 2026-06-29. These dates do not change merely because this article is rebuilt.